Tesseract runs Claude Code in a private sandbox and puts the whole machine in your pocket: agents, builds, terminals and a live display.
Works with the stack you already ship. Android, Electron, web and more.
Tesseract is a new kind of development machine. It lives in a container on your own server, runs Claude Code around the clock and answers to your phone. Ask for a change, approve it from your Lock Screen and download the build, wherever you are.
Claude Code that keeps working when you put your phone down
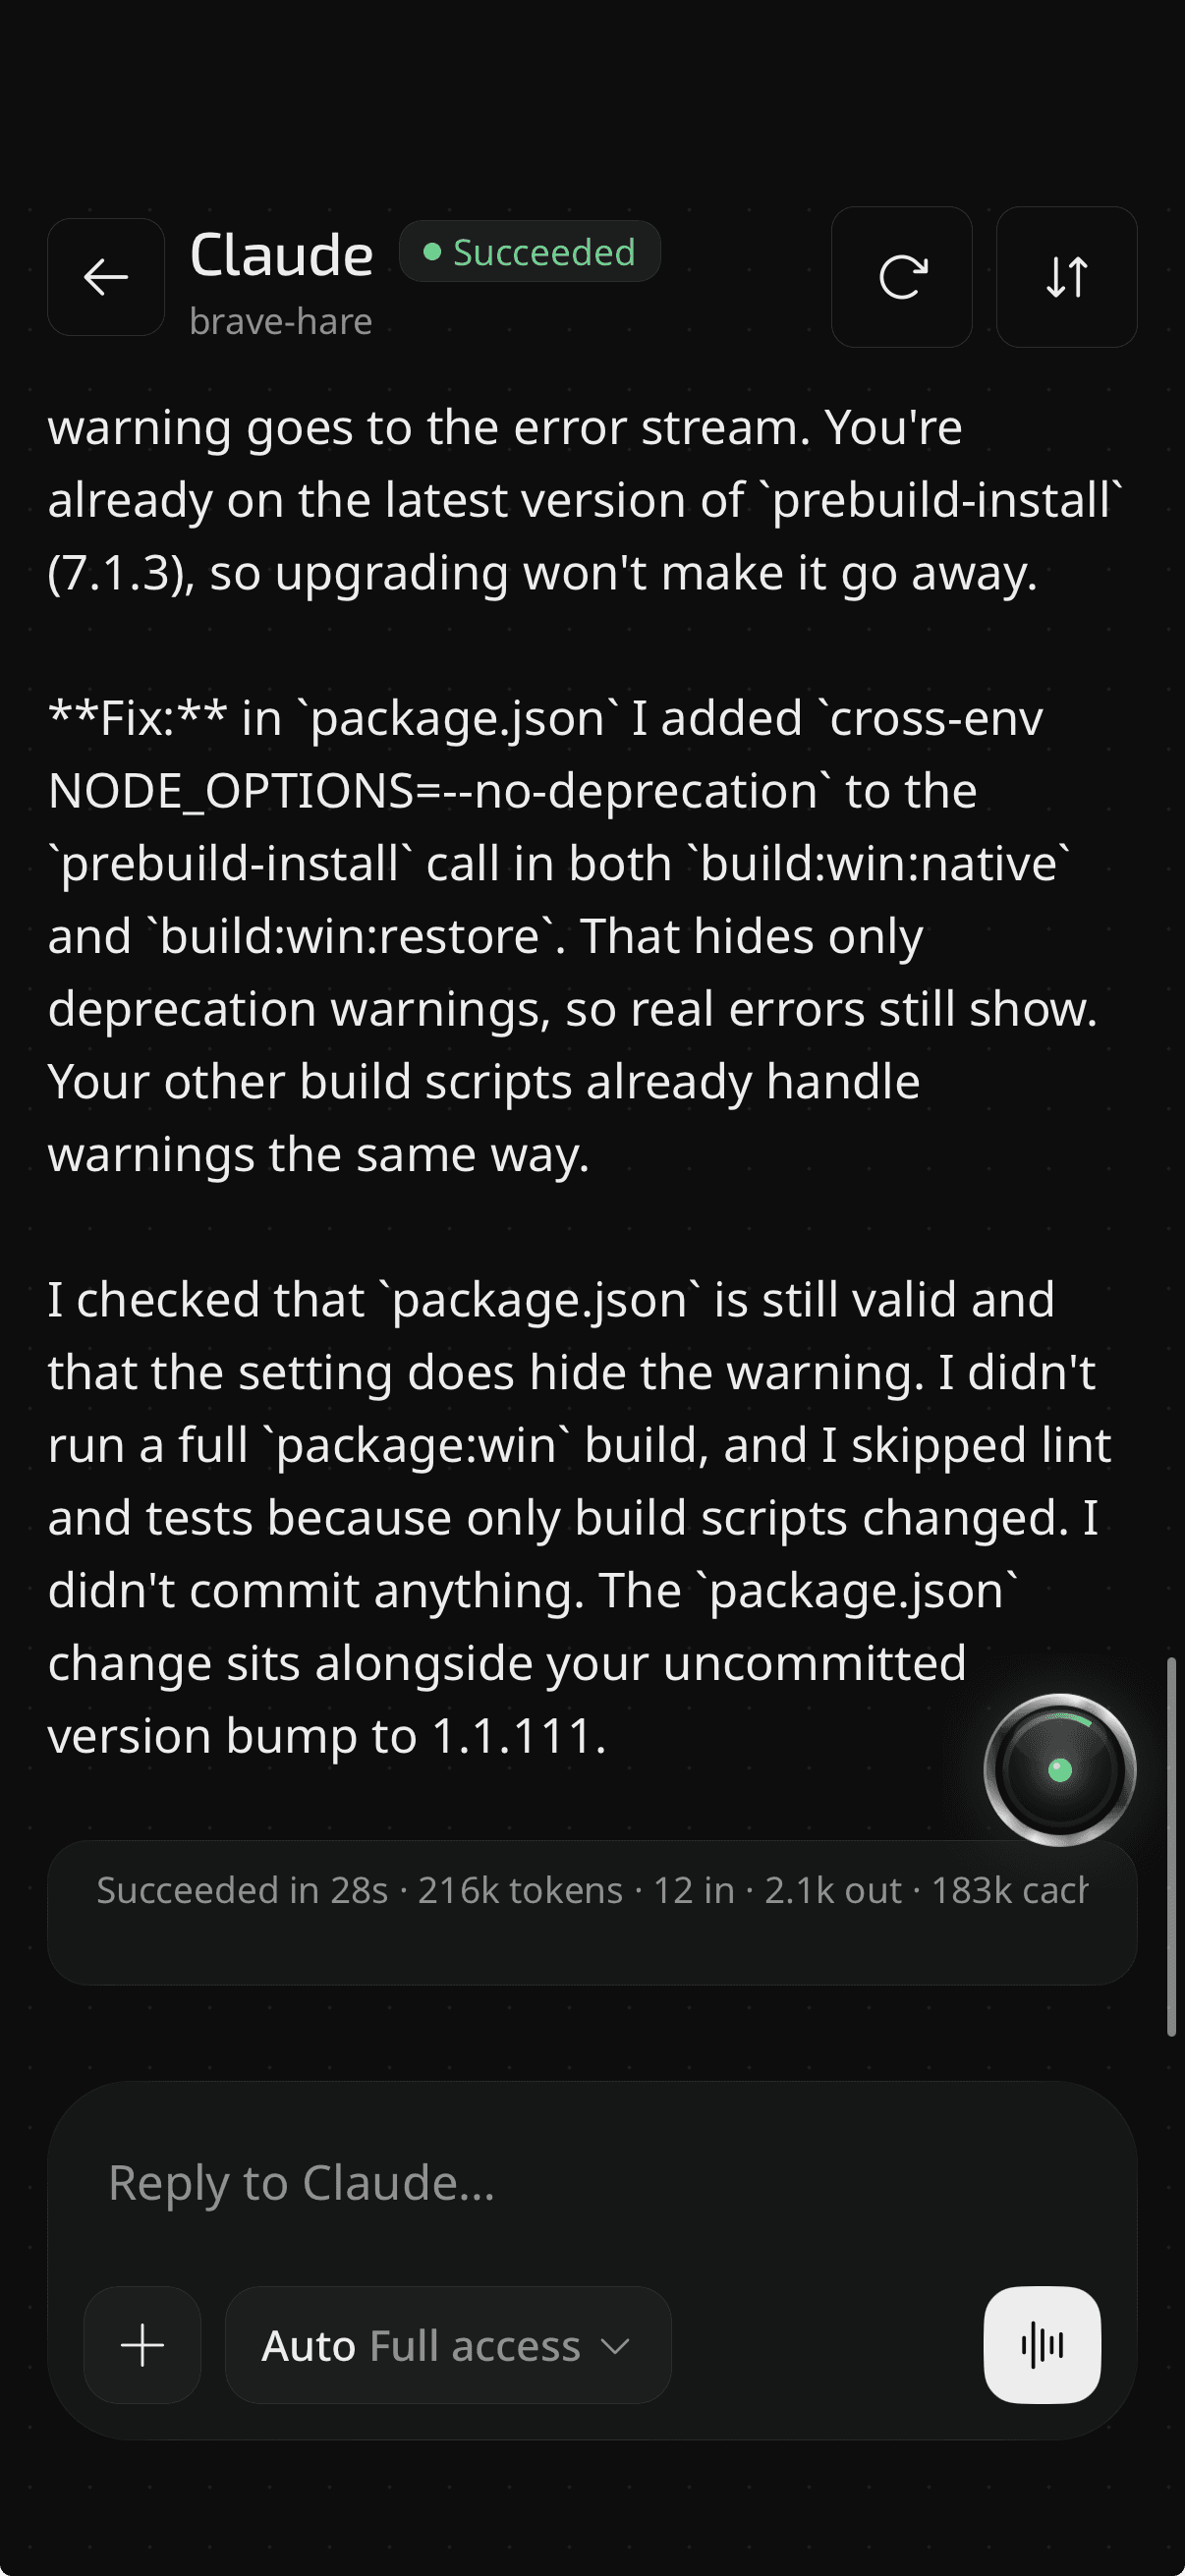
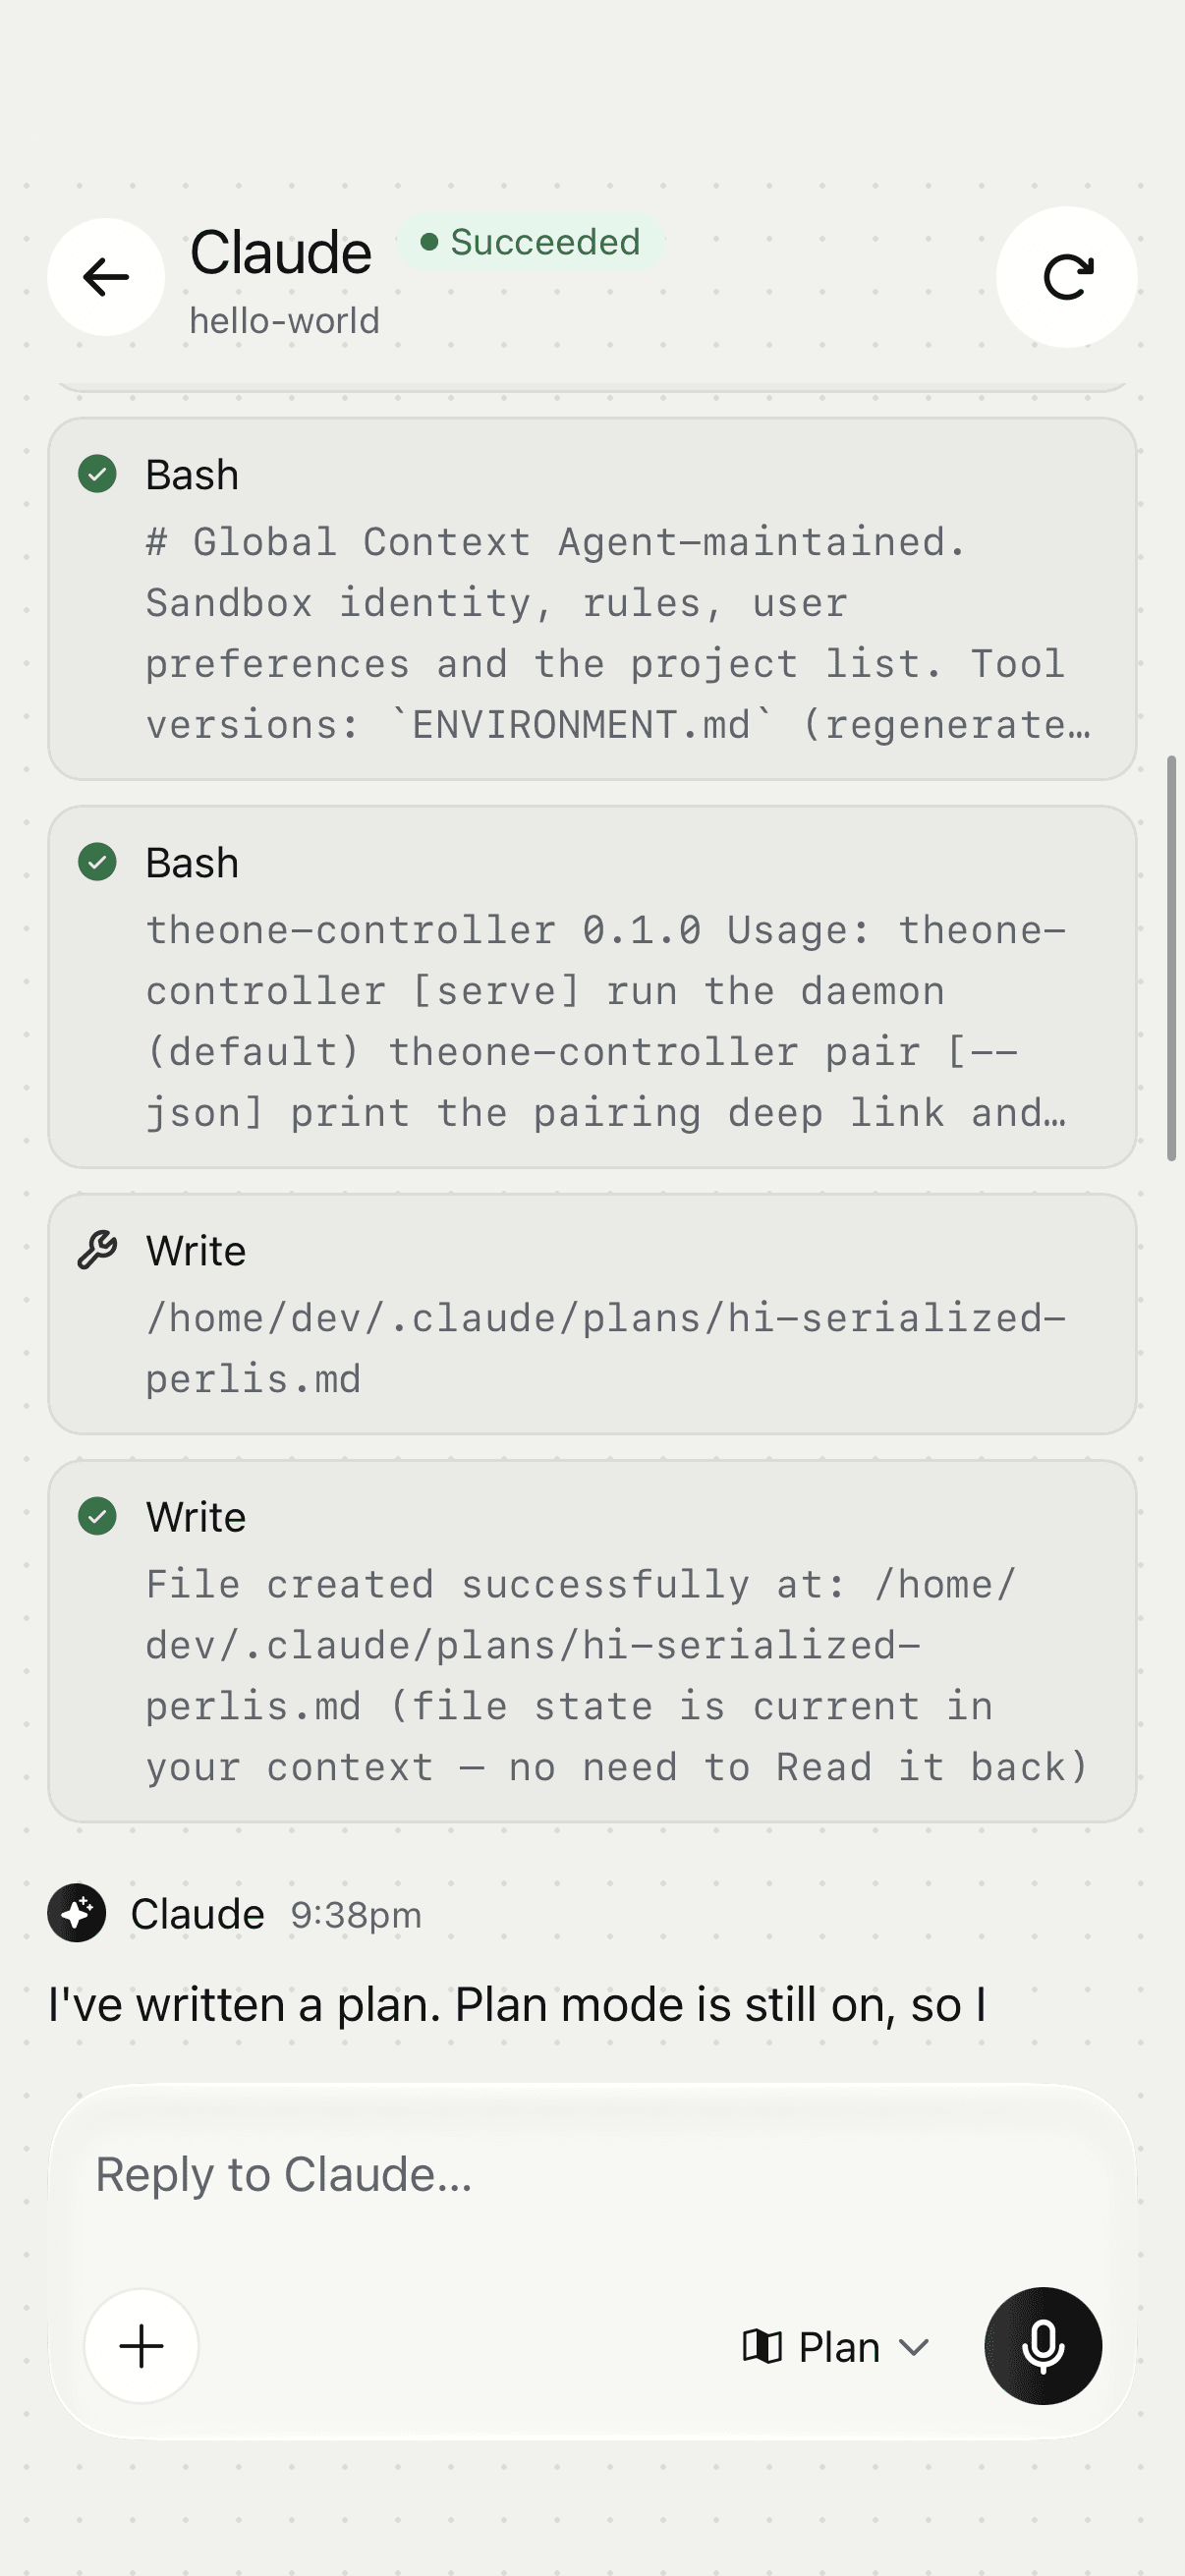
Start a run from anywhere and follow every tool call, diff and test result as it streams in. Claude works inside your sandbox, with your repos, your toolchains and your tests.
- Read
src/auth/session.ts - Edit
session.ts +12 −4 - Bash
bun run test84 passed - Build
android-apk · release64%
- FIG 1.1
Live tool steps
Bash, edits and writes stream in as Claude makes them.
- FIG 1.2
Plan or full access
Pick a mode per run and switch models on the fly.
- FIG 1.3
Talk instead of type
Voice prompts are transcribed inside your sandbox.
Only the things that need you
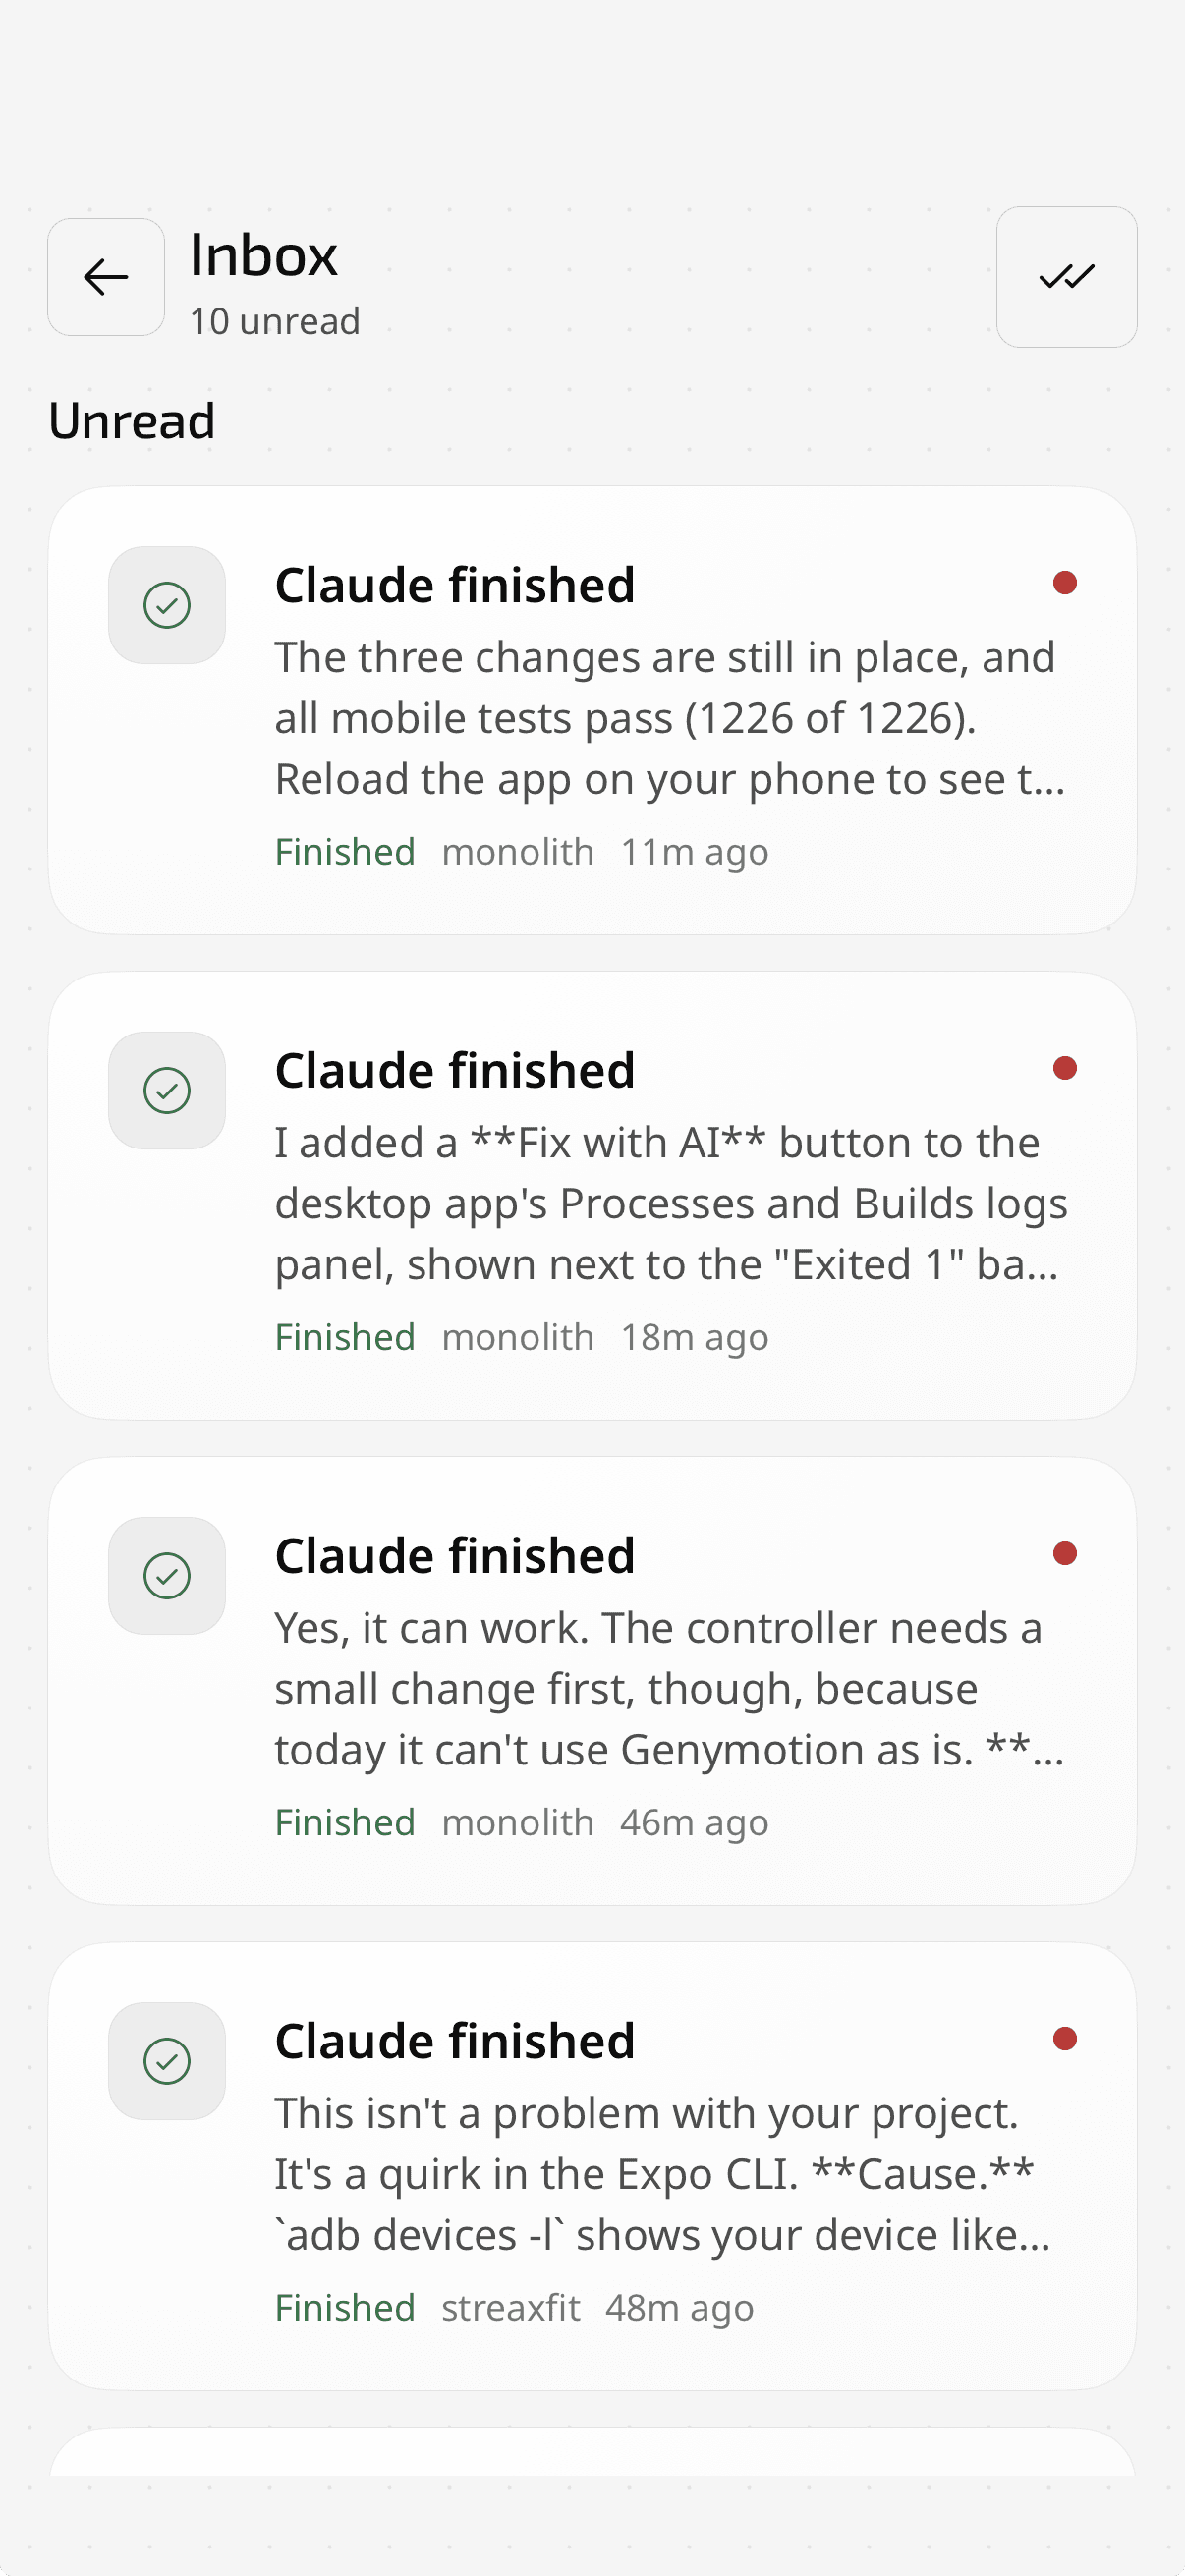
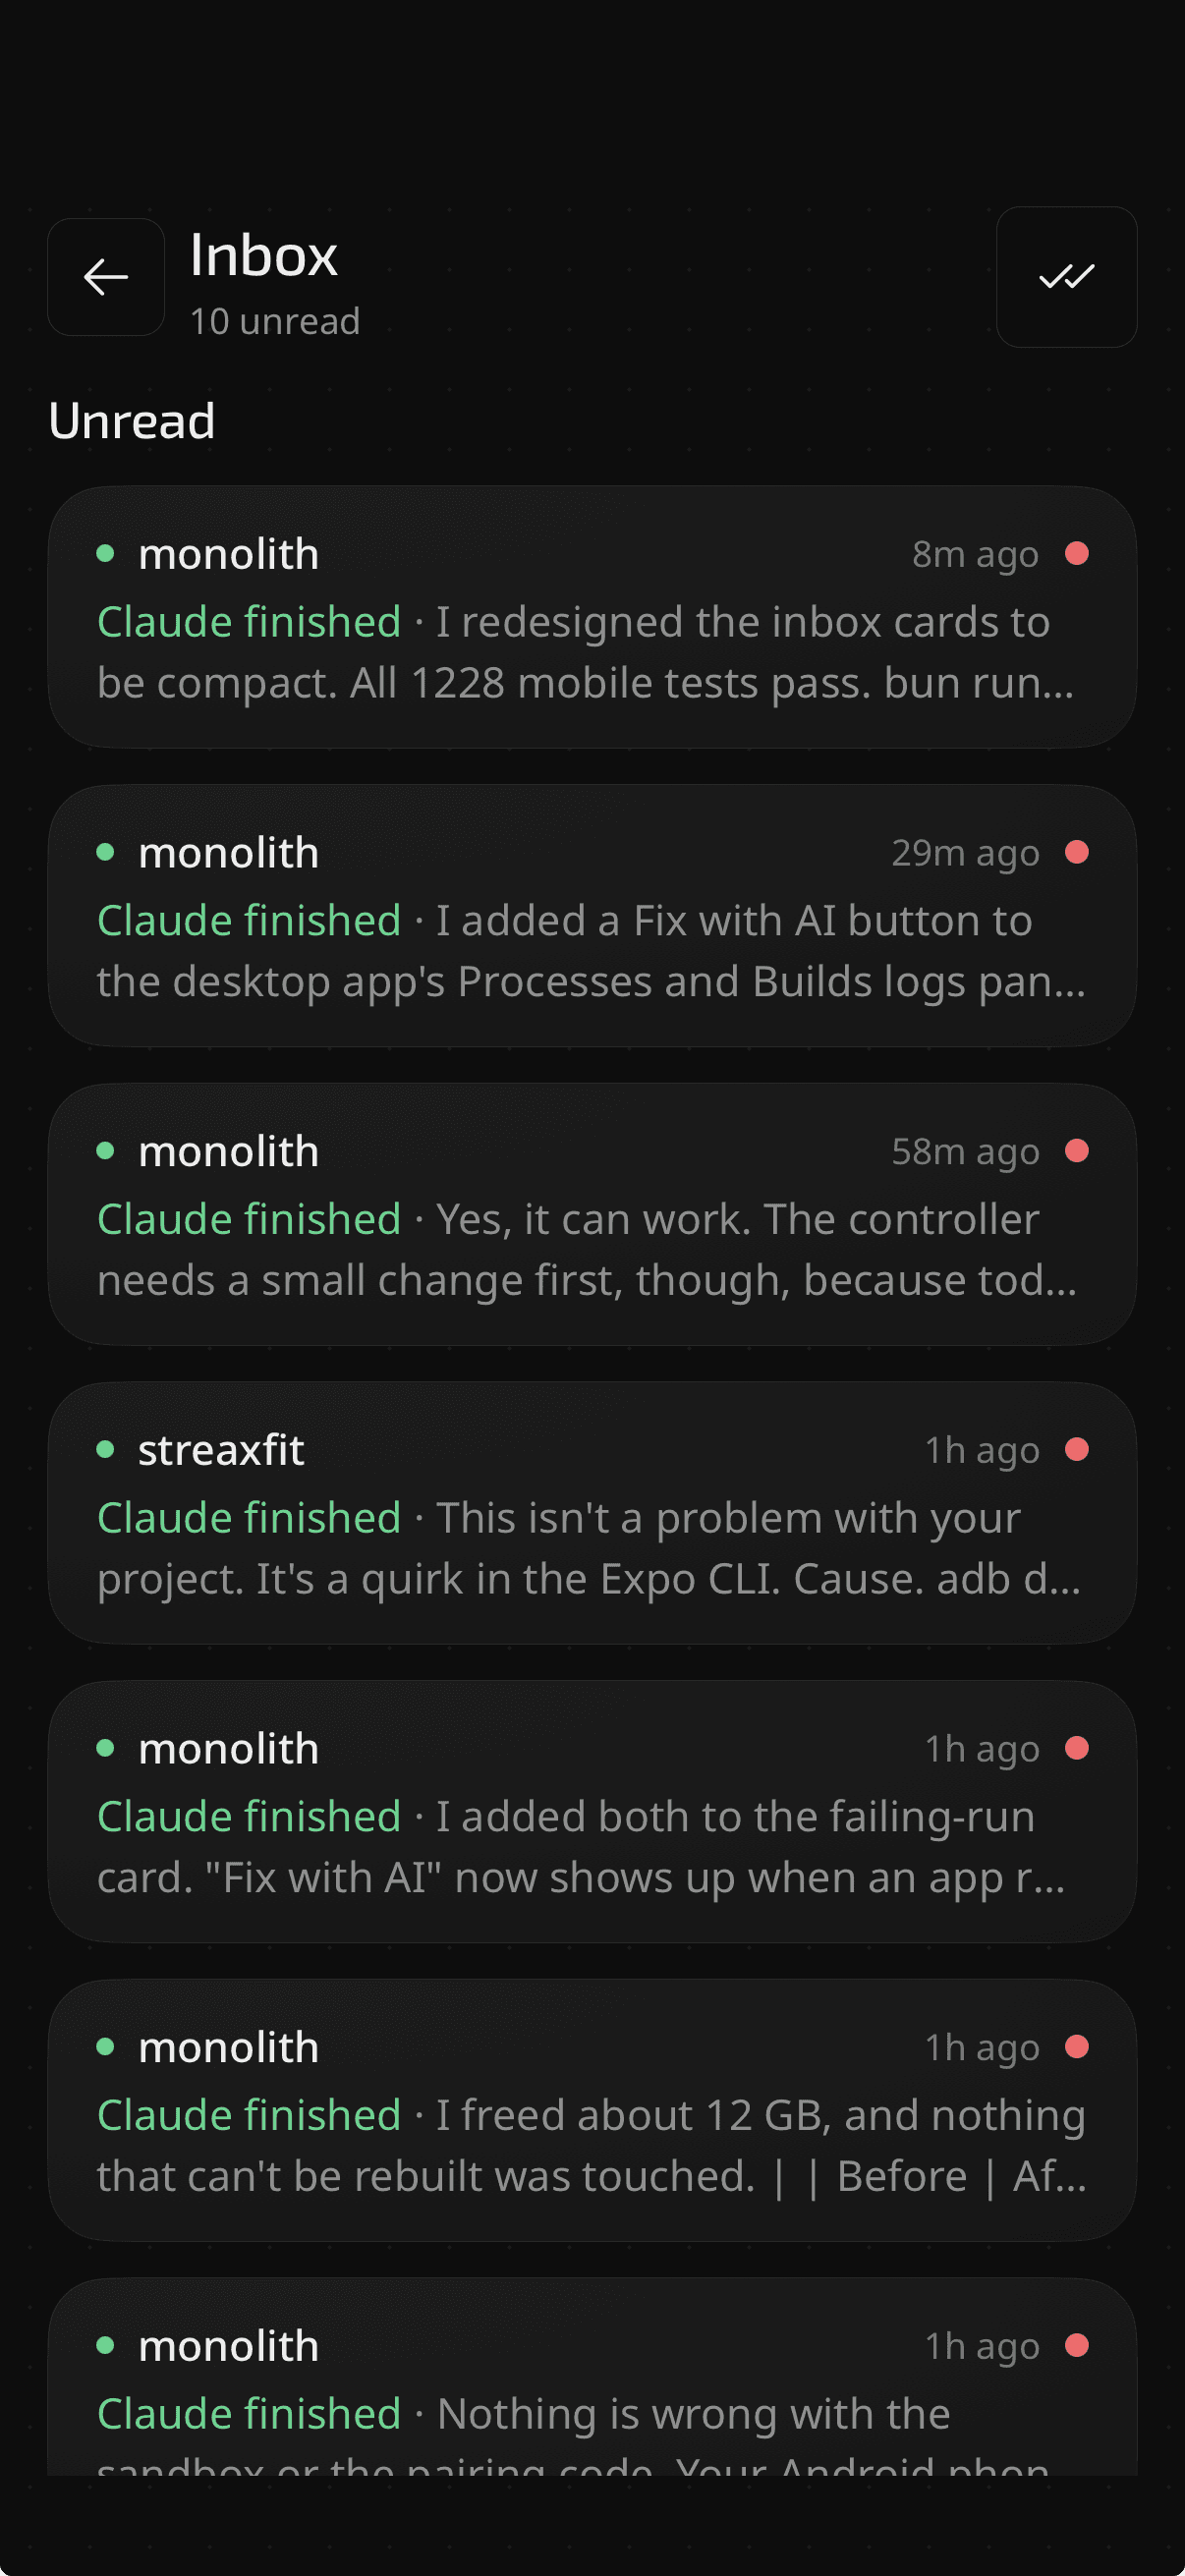
Permission prompts, questions and finished runs land in a single inbox. Approve with a tap, and Claude picks up where it stopped.
- FIG 2.1
Remote approvals
Allow or deny a tool call without opening a laptop.
- FIG 2.2
One push per run
Each finished run sends exactly one notification.
- FIG 2.3
Live Activities
Build progress on the Lock Screen and in the Dynamic Island.
Every project, build and port in one place
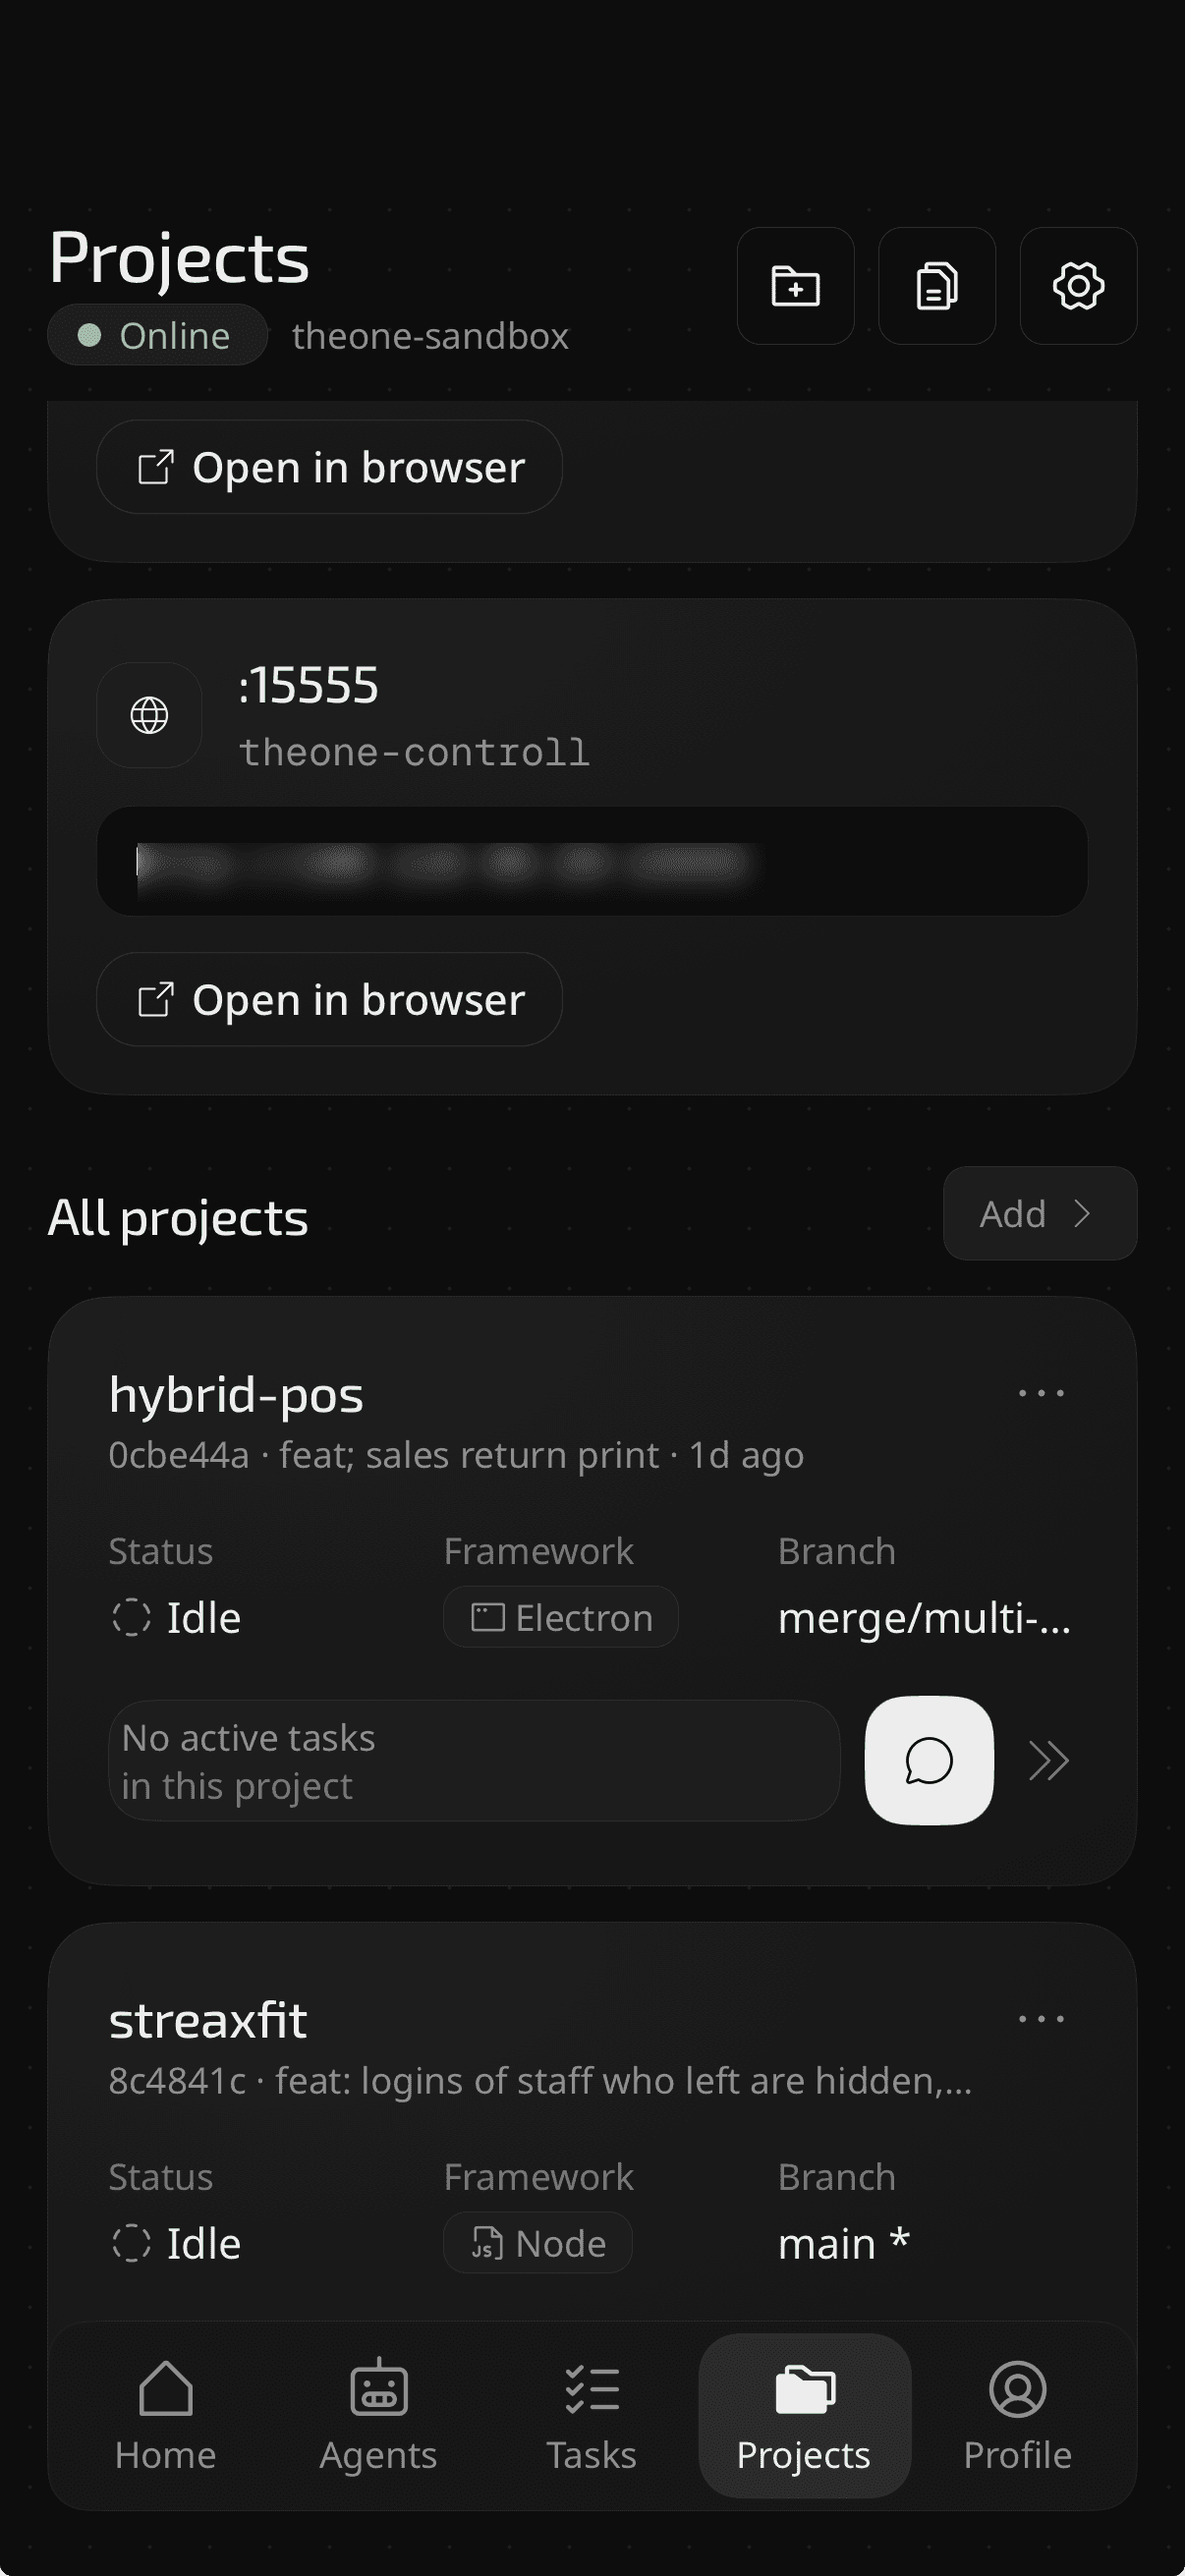
Clone a repo, queue a build and keep dev servers running even when your phone disconnects. Finished artifacts come with a checksum and are ready to download.
- Install18s
- Prebuild41s
- Gradle assembleRelease2m 06s
- Verify & copy artifact
64%sha256 9f2c…b41e- FIG 3.1
Real builds
Android APK and AAB, Linux AppImage, Windows installers and web.
- FIG 3.2
Verified artifacts
Every artifact gets a SHA-256 and a predictable name.
- FIG 3.3
Ports on your tailnet
Open a running dev server straight from the app.
Your machine, on your network
The sandbox is reachable only over your Tailscale network, and every request is authenticated. The host just runs Docker. Nothing is exposed to the internet.
- FIG 4.1
Tailnet only
WireGuard end to end. No public ports, no tunnels.
- FIG 4.2
Token auth
Every request and socket is authenticated.
- FIG 4.3
Clean host
Toolchains, caches and secrets stay in the container.
And everything else a development machine needs
Live display
Watch and drive the sandbox desktop over VNC.
Real terminals
Full PTYs that keep running after you disconnect.
Files & Taildrop
Browse outputs and send them to any device.
Usage
Token trends by day, project and session.
Multiple accounts
Pick the Claude account for each project.
Desktop companion
A native Linux app for the same sandbox.